Skip to content

Your users’ data never leaves Europe.

100% hosting in France, analysis by a French artificial intelligence, GDPR compliance by design — not by contract amendment.

  • 100% in FranceScaleway and OVH
  • Analysis by MistralNo American model
  • GDPR, ISO 27001AI Act, outside the CLOUD Act

The sovereignty question comes up early in the sales cycle.

Compliance, CISO, DPO: on feedback, behavioral analytics or AI projects, the question “where does our data go?” is no longer secondary. It determines whether the contract gets signed — and it blocks deals when the answer is vague.

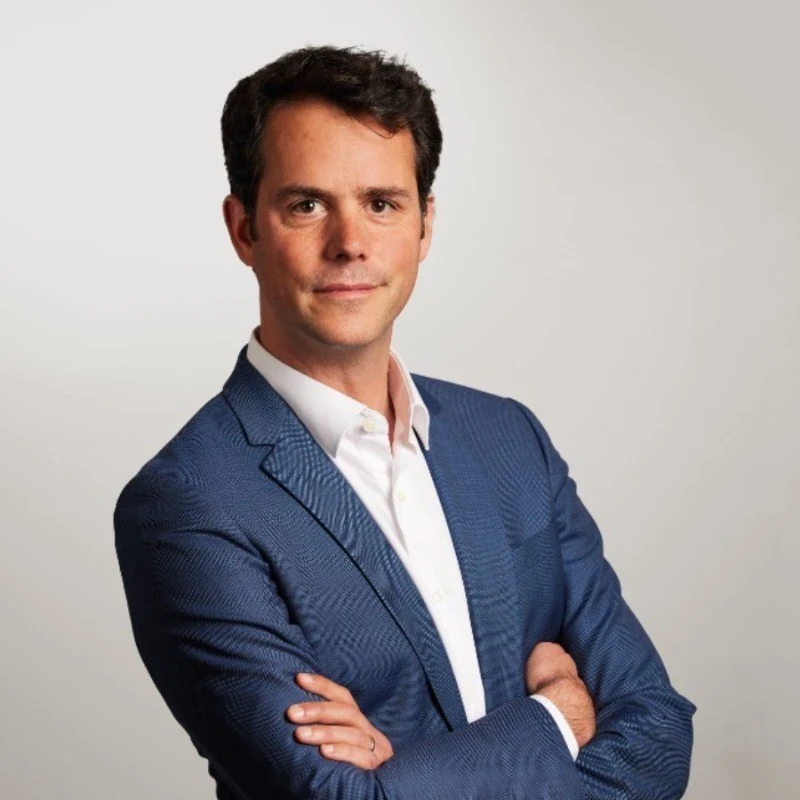
Portrait de Pierre Machoel
“As an international automotive group, compliance and data protection are essential for us. Working with a European company was therefore reassuring for us.”
Pierre Machoel · Digital Performance & Content Manager · Nissan AMIEO
  • 100%of data hosted in France, sessions and responses included
  • 0cookies set and no IP address stored by default
  • 0American models in the AI analysis chain

Four questions, four verifiable answers.

A customer’s open-ended answer, a recorded session, a survey response: this is data that can contain an address, a medical reason, the precise behavior of an identifiable user. It is never trivial, and the answer to “who has access to it, and under which law” must be verifiable, not just declared.

  1. Where the data is stored

    100% in France

    Scaleway and OVH, two French hosting providers. Your data, including recorded sessions and survey responses, stays in the country: no replication, no backup, no processing outside France.

  2. Who analyzes it

    A trusted AI

    Having an AI analyze the voice of your customers must not create the very risk the rest of your compliance work tries to avoid. Analysis runs on Mistral models — a French company, with data hosted in Europe — and your data is not used to train the models. No American model is involved anywhere in the chain.

  3. Which law applies

    Outside the CLOUD Act

    A hosting provider or software vendor subject to US law can be compelled to hand over data to a US authority, even when it is stored in Europe, including through its European subsidiaries. Screeb, a French company, has no such obligation.

  4. What we don’t collect

    Privacy by design, not as an option

    By default, Screeb collects no personal data, sets no cookies and stores no IP addresses. It’s not a setting to turn on: it’s the factory default, and it’s what makes the consent exemption mode possible.

Six settings for the most constrained organizations.

Where data is hosted and where the intelligence analyzing it comes from are two of the first things an impact assessment looks at. Both are set by default. On top of minimal collection, there are levers to turn on depending on your framework.

  1. Automatic redaction of personal information in open-ended answers and analyzed conversations — anonymization happens before the analysis, not after the fact.
  2. A consent exemption mode for organizations that legally qualify for it.
  3. A dedicated environment, separate from other customers, when your risk analysis calls for real isolation and not just logical isolation: your own domains, databases shared with no one, and authentication of your own.
  4. Data that stays in the country, for public bodies and their contractors, whose tenders often require hosting in France and not just in the European Union.
  5. HDS-certified hosting, for health data, with the retention and service commitments that come with it.
  6. Session replay off by default, to be turned on explicitly — so it can go through CISO or DPO approval before anything is recorded. Sensitive fields are masked automatically.

Where your users’ data lives, tool by tool.

A public buyer, a bank or a hospital must be able to answer a simple question: which law do my users’ responses fall under, and who can access them? Here is what the platforms we are compared with publicly state.

Tool Where data is processed The risk for your compliance
France — Scaleway and OVH. Analysis by Mistral, in Europe. European law end to end, out of the CLOUD Act’s reach.
United States, with an optional European region depending on the contract. US vendor: the parent company remains subject to the CLOUD Act, whatever region is chosen.
United States, with optional European residency. US vendor: same exposure to extraterritorial law.
United States, with an optional European region depending on the contract. European hosting doesn’t put the vendor outside US law.
United States, with optional European data centers. US vendor, controlled by US shareholders: the CLOUD Act applies to the parent company.
United States, with optional European data centers. US vendor: same exposure to extraterritorial law.
United States — the platform now belongs to the Qualtrics group. US vendor: same exposure to extraterritorial law.
Ireland, on AWS or Microsoft Azure, with an optional US region. French vendor. French vendor, but US hosts (AWS, Microsoft) subject to the CLOUD Act, and support access from outside the EU in the subprocessor list.

“Hosted in Europe” is not enough.

Several tools in the table above offer a European region. But where the servers sit does not change the law the vendor answers to. The CNIL, France's data protection authority, has said so at least twice.

2020Health Data Hub

In its submission to the Conseil d'État, the CNIL found that choosing a host subject to US law “seemed incompatible” with the requirements of the Court of Justice of the European Union. It recommended switching operators or providing specific safeguards.

Read on cnil.fr
2023Deliberation #2023-068

Using a subprocessor subject to extraterritorial law means checking whether its country's laws let foreign authorities access the data. The CNIL strongly recommends that no access by foreign authorities be possible.

Read on Légifrance

ScreebNo non-European law

A French company, French hosts (Scaleway and OVH) and analysis by Mistral. No link in the chain is subject to the CLOUD Act.

Hosting in France was simply a must-have for us.
Photo de Romain GentetEdificeRomain GentetLead Product Manager · Edifice

What your DPO can verify about the AI.

AI analysis is at the heart of Voice of Customer. It must not become the weak point of your compliance, so here is what you can verify, piece by piece.

  • What goes to the modelFeature by feature.Feedback analysis sends the questions and answers. Follow-up questions, the survey description and the answers already given. Tagging, the text and your list of tags. Session summaries, the pages visited and the clicks. Nothing else is sent.
  • One model per taskYou choose the provider.Screeb then picks the right Mistral model for each job (a light model to classify, a larger one to summarize) so you don't have to weigh every detail.
  • Your own modelOn your own endpoint.Organizations that already run their own instance can plug it in with their key: the analysis then runs on your side, and nothing leaves your perimeter.
  • A logged choiceAnd a reversible one.Every provider change is timestamped and attributed. And AI stays optional: it can be removed from your workspace on request, without touching the rest of the platform.

For your CISO, your DPO and your procurement team.

The documents your security review will ask for are here.

  • The documents: data processing agreement, subprocessor list, details of encryption at rest and in transit, and answers to your security questionnaires.
  • Your data stays yours: export at any time, deletion on request, configurable retention period.
  • The action log: who did what, and when. Sensitive actions (export, deletion, settings changes) are timestamped and attributed, so your DPO can trace them without calling you.
  • One less blocker: a vendor whose hosting, AI and jurisdiction are European removes the step of the approval cycle that often pushes a project back by a quarter.
Frequently asked questions

Your questions.

Where exactly is our data hosted?

In France, with Scaleway and OVH: two French hosts, with no dependence on a US cloud.

Is session replay GDPR-compliant?

Yes: sensitive fields are masked, explicit activation is required, and no data leaves France.

What is the CLOUD Act, and why does it matter?

A US law that can force some cloud providers to hand data over to US authorities, even when it is hosted in Europe, if the provider is American. Screeb is not exposed to it: neither the hosting (Scaleway, OVH) nor the AI (Mistral) is under US law.

Is Screeb ISO 27001 certified?

Yes. Not to be confused with the certifications of our hosts OVHcloud and Scaleway, which are their own.

Does Screeb comply with the AI Act?

Yes. The AI processing Screeb performs on your data is documented and falls under the European framework.

How do we start a security review with our CISO?

Book a demo or contact us: the team answers security questionnaires and assessment grids.

Does this page cover accessibility and carbon footprint?

No, those two topics have their own pages, because they speak to other readers and rest on other evidence. Accessibility of surveys and messages (RGAA and WCAG criteria, automatic checks on every change) is covered on the Accessibility page. Screeb's share of your carbon footprint is on the Carbon Footprint page.

A question from your CISO or your DPO?

Let's talk it through. In 30 minutes, review the hosting, the AI and the jurisdiction, with the documents to back it up.

Shall we fill in your security questionnaire together?